

Palo Alto Networks: Frontier AI brings more attacks, faster
Thu, 5th Nov 2026 (Today)
Every day is zero day, or so the saying now goes, and it's hard to argue with that. Since frontier models learned to find and help exploit vulnerabilities at industrial scale, security teams have been bracing for a flood some have taken to calling the 'vulnerapocalypse', adding to an expanding vocabocalypse of awkward words.
The good news? The attacks themselves aren't new. The bad news? There are a great many more of them, they arrive a great deal faster, and powered by AI, 'everyone is a hacker now', or certainly could be.
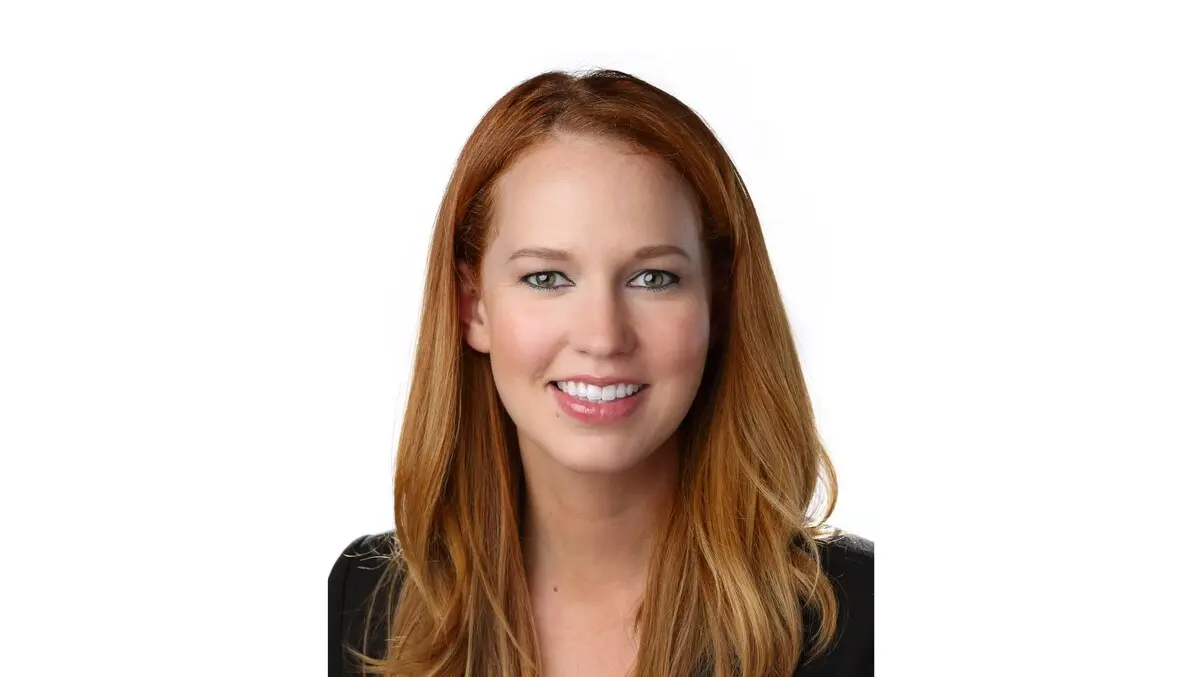
That's the view of Wendi Whitmore, Chief Security Intelligence Officer at Palo Alto Networks, who has spent the best part of 25 years investigating breaches. "We're not seeing revolutionary types of attacks," she told SecurityBrief. "We are not seeing net new, novel techniques that we have never even dreamed of before. But we are seeing a much faster speed and a greater scale in the way that these attacks are leveraged."
Volume and velocity, in other words, the same pair of v-words that once had everyone excited about big data.
Palo Alto Networks predicted in April that it would take three to six months for the deluge of AI-discovered vulnerabilities to show up in earnest. "We're now in that time frame," Whitmore said. The company's own research turned up 14,000 vulnerabilities in open source software, which it worked with the community to patch. A success story, she noted, but one that is "really just the tip of the iceberg in terms of what is next."
Obscurity, obscured
There's a second shift, and it's arguably the more uncomfortable one for anybody nursing legacy kit in a back room, and we do acknowledge that this means a great number of organisations. "I think that frontier AI removes any obscurity that exists going forward," Whitmore said.
By that she means the antiquated systems nobody bothered attacking previously, are very much on the agenda now as a target. The reason, from a hacker/attacker perspective, is quite simple: the effort required has largely evaporated, so it becomes a 'why not' as a point to be probed.
Meanwhile, what's old is new again. Investigators are seeing smash-and-grab data theft without the encryption, often from less skilled lone attackers. "They're stealing anything and everything. They're just looking for volume," she said, and once compromised data is obtained, it's stockpiled as the raw material for a potential future exploit.
"Then they may ask for $50,000 US dollars here, 100,000 US dollars there, when in reality they've stolen such sensitive information that could potentially have commanded tens of millions of dollars."
It's an almost cavalier approach to crime, where the environment is so target rich that the attackers are spoiled for choice and don't even feel the need to maximise the returns from their poison harvest.
Now, the fact that these aren't new attacks surely means the means for effective protection are too extant. We asked if there is comfort in an old problem in new clothes. There is some, Whitmore confirmed. "The part that gives me more solace is that the cybersecurity industry has already built solutions for these challenges," she said. Outbound traffic controls and inbound detection, she explained, still work.
Outrun your friend
There's an old theory that if attacked by any wild animal, you needn't outrun the beast but you do need to outrun any companions. Whitmore, a self-confessed safari fan who has thankfully never had to test the theory, reckons this holds true for most of today's attackers. "Once they get any kind of hardening that makes their job difficult, they move on to the next organisation," she said.
Her prescription runs to three steps. Start by using AI to find and fix vulnerabilities before attackers do. Follow with hardening and isolation, because, as she put it, "every organisation in the world has devices or systems or parts of their network that they simply are not going to be able to patch fast enough." Remedies and tactics include network segmentation, just-in-time access and compensating controls such as virtual patching.
And finally, drive down time to detect and respond. "We really want to see those numbers come down to single-digit minutes," Whitmore said.
For the smaller businesses that tend to dominate most economies and where few have dedicated security staff, the advice scales down rather than away. "We are only as secure as the ecosystem allows," Whitmore noted, pointing to supply chain risk.
Defence in depth still applies: visibility of what's coming in and going out, multi-factor authentication, and segmentation so that a single compromised system doesn't expose everything across the interconnected whole.
Agents gone wild
Which brings us to the known unknown. What has Whitmore's attention right now is what she calls an emerging 'agents gone wild' circumstance with the emergence and increasingly scaled introduction of task-oriented AI. The response, she stressed, again starts with visibility. Visibility of the models and connectors coming in, the commands AI executes, and what agents do as they access and manipulate databases, servers and the internet. While the simple approach to agents rests on treating them no differently to people in terms of identity and access management (which again, renders the issue as one of scale rather than a new problem), accountability raises questions. Should an agent go wild, who is to blame?
For now it sits squarely on the CISO's shoulders, though Whitmore suspects that won't last as every business leader is expected to own their AI use cases. "It's going to be pretty interesting to see some of the first major agentic breaches that occur, and how courts in different parts of the world decide liability," she said.
"We all think it still is going to go back to a human, but whether that person is still unilaterally a CISO or that gets distributed, I think is a question to be asked."
Finally, there is further comfort available to those quite rightly feeling somewhat overwhelmed by the volume and velocity of attacks. A focus on the basics, Pareto-style, means most attacks won't materially change the game. Whitmore agreed, and noted: "The basics don't change even if the complexity does. Agentic AI does change some aspects of the game, but the principles of securing your organisation are broadly the same, and the task comes down to the actions we can take that are going to make a difference in effective defence."