

Only 2% trust AI-ready cyber recovery, survey finds
Thu, 17th Sep 2026 (Today)
Cohesity has published research showing that only 2% of Australian organisations believe their recovery plans can withstand threats posed by frontier AI technologies. The findings also place Australia among the most targeted countries for cyberattacks in the study.
The survey found that 80% of Australian organisations suffered a material cyberattack in the past 12 months, compared with 73% globally. Overall, 95% said they had been affected by a material cyberattack at some point.
Almost all Australian respondents, 99%, said they had a cyber resilience strategy in place. Yet 53% said it still needed improvement, including 9% who said significant improvement was required.
Among organisations that had experienced an attack in the past year, 93% said they still relied on recovery plans based on unproven assumptions. Another 92% believed their recovery plan would require workarounds or improvisation during an incident.
Recovery times also appeared to be under pressure. The report found that 87% took longer to recover than expected, by about five hours on average, while 74% said more systems were affected than initially assessed.
Recovery gaps
The research pointed to a mismatch between formal planning and operational readiness. Many organisations said their recovery plans assumed attacks would be contained before recovery began, dependencies would be clearly understood, recovery would follow a largely linear process, decision-makers would have enough information, and the environment could be trusted when restarting operations.
According to the findings, those assumptions often broke down during real incidents. More than half of respondents reported significant gaps in their response and recovery plans during a cyberattack.
The most commonly cited gaps were skills and knowledge, named by 70% of respondents; identity and access management tools such as Okta, cited by 67%; and AI models, pipelines and workflow tools, cited by 65%.
Attention is also turning to what the report called a Minimum Viable Company, or MVC, approach. The framework identifies the minimum people, processes and technology needed to keep essential business functions operating while broader recovery work continues.
While 74% of Australian organisations said they had identified the critical functions needed during a disruption, only 20% said they had both formally documented and tested an MVC plan. That compares with 22% globally.
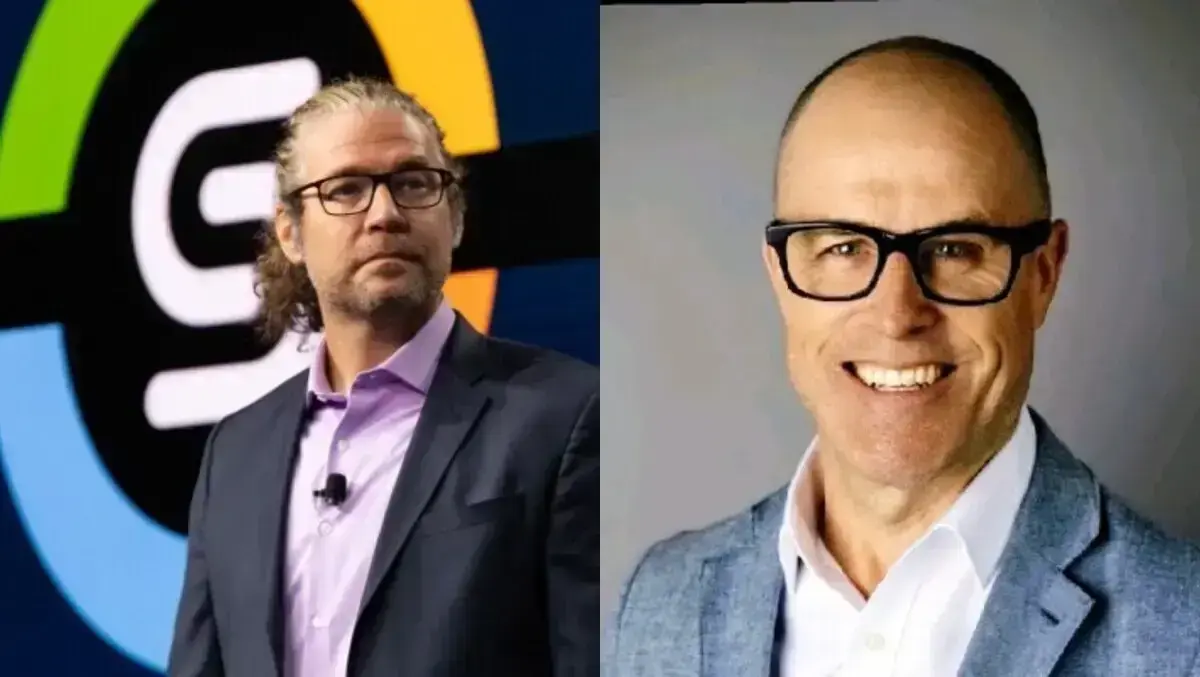
James Eagleton, Managing Director ANZ, Cohesity, said business continuity now sits at the centre of cyber planning.
"The challenge for leaders is no longer simply preventing an attack. It is ensuring the business can continue to operate and recover with confidence when an attack breaches the defences," Eagleton said.
"Australia's focus on Minimum Viable Company planning is encouraging, but identifying critical operations is only the first step. Organisations must formally document and regularly test whether these plans can support the business under real-world attack conditions. That requires realistic resilience strategies, because recovery is rarely straightforward. More systems may be affected than initially expected, and leaders often need to make critical decisions with incomplete information. In real-life scenarios, organisations with a proven and tested cyber recovery plan can be more confident, as this nullifies the leverage an attacker will attempt to use," he said.
AI exposure
The report also highlighted weak visibility into the use of AI inside Australian organisations. Nearly half, 47%, said they did not have a centralised inventory or clear understanding of the AI agents, copilots and workflows operating across their business.
Only 40% said their cyber response and recovery plans comprehensively covered scenarios targeting AI systems, workflows or models. Just 38% said they were very confident they could verify the integrity of AI models and related data after an incident.
Confidence in managing operational failures involving AI was also limited. Only 44% of Australian organisations said they were prepared to detect and contain unintended or incorrect actions taken by AI agents, copilots or AI workflows, and to recover affected systems or data.
That suggests AI adoption is moving faster than cyber recovery planning in many businesses. As AI tools become embedded in operational processes, gaps in asset visibility and data verification could complicate recovery after an attack.
The study was conducted by Vanson Bourne on behalf of Cohesity and surveyed 3,200 IT and security leaders across 12 countries, including Australia, the UK and the US. It defined a material cyberattack as one with measurable financial, reputational, operational or customer churn impact.
Greg Statton, VP and CTO APJ, Cohesity, said AI can help organisations move faster and improve how they identify and respond to threats.
"But it also expands what they need to understand, secure and recover. If a business cannot identify the AI systems and workflows it relies on, or verify the integrity of the data and models behind them, it is difficult to trust that the data after an incident is actually safe and clean. Ultimately, trusted AI depends on trusted data," Statton said.