Offensive Security stories
Smaller firms could face more frequent attacks if access to advanced models stays limited to government agencies, Huntress says.
Australian firms could get a clearer view of AI-driven attack paths as ThreatCanary rolls out a platform blending asset discovery, API checks and offensive testing.
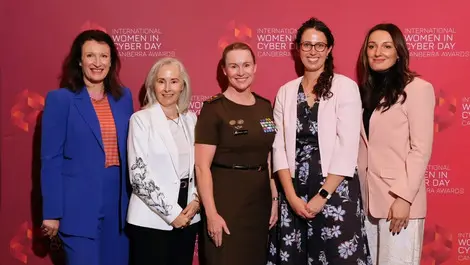
Skills shortages in Canberra's cyber sector are being tackled through awards for women, mentors and employers boosting inclusion.
Tracebit found the altered open-weight model reached admin rights far less often than the original, raising doubts about its attack utility.
The deal gives security teams a widely used AI testing tool with on-premises controls, as vendors race to speed up offensive defence.
The service keeps source code inside customers' AWS environments while using human review to cut false positives and verify fixes.
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Targeted phishing and payment fraud are getting harder to spot as attackers mimic routine business workflows and trusted contacts.
Criminals are increasingly using AI for ransomware and credential theft, while flaws in test models are exposing production systems and data.
Security teams can now compare validated exposure findings with endpoint and cloud telemetry after Horizon3 tied NodeZero into CrowdStrike's SIEM.
Defenders now have minutes, not hours, as attackers use agentic AI to automate credential theft, scanning and extortion across live operations.
UK and Ireland resellers gain access to 24/7 threat hunting and incident response as eSentire widens its channel reach through CMS Distribution.
Security teams could cut manual triage as the new service ranks code and intrusion risks by real-world exploitability, not alert volume.
The funding will help Lasso expand a guardrail designed to inspect AI traffic at scale without costly GPUs, including for US government users.
Security teams can now trace how one weak point becomes a full breach path as Filigran automates multi-step testing in OpenAEV v3.
The deal gives A-LIGN customers direct access to penetration testing and red teaming as firms seek fewer vendors for cyber compliance and defence.
Enterprise buyers are spending more to secure AI agents, with Snyk saying Evo now drives 60% of new deals and larger contracts.
Smartphone apps used for banking and workplace access will face tougher defences as the partners recruit two cybersecurity researchers for a 30-month project.
US banks are under pressure to prove systems can be restored quickly as regulators and counterparties demand tested resilience, not paper plans.
The tie-up gives enterprise and government clients deeper testing coverage as AI reshapes offensive security and demand for specialists grows.