

ThreatCanary launches sovereign AI security platform
Tue, 15th Sep 2026 (Today)
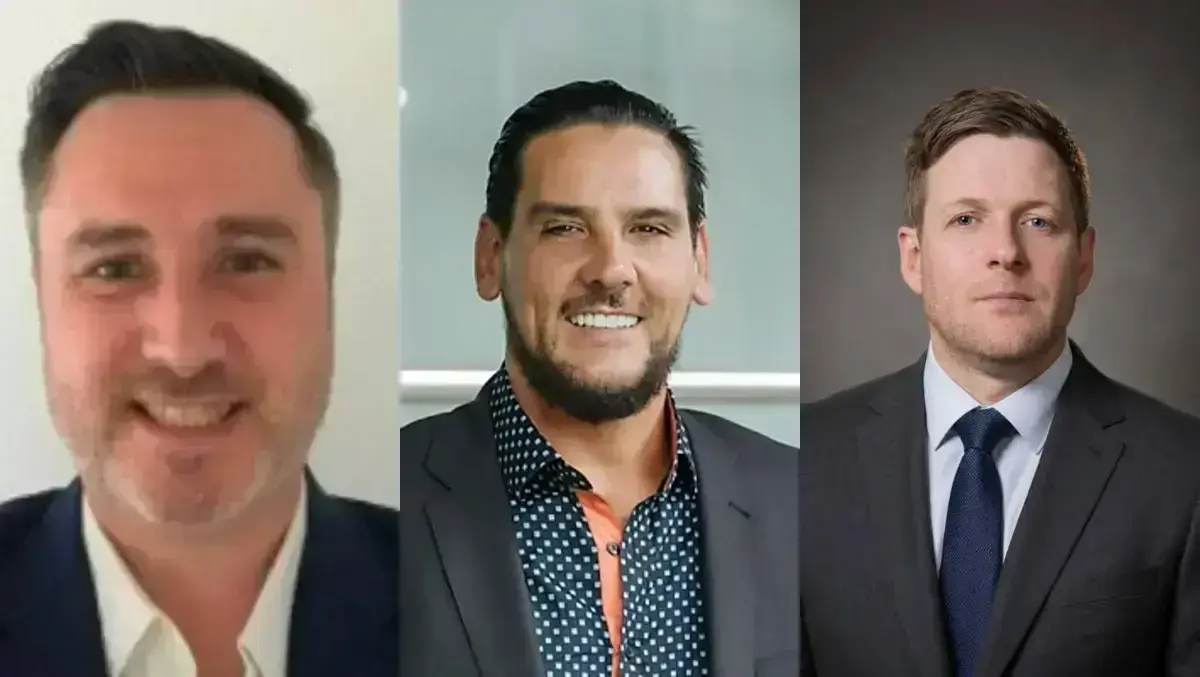
ThreatCanary has launched an Australian sovereign, AI-native offensive security platform and named Marco Delgado as Co-Founder and Chairman.
The Sydney-based business is entering the market with a platform that combines External Attack Surface Management, API Security, and Autonomous Offensive Security in a single system designed to help organisations identify potential attack paths.
ThreatCanary was founded by Matt Flannery, Chief Executive Officer, and Andrew Horton, Chief Technology Officer. Delgado, whose previous ventures include Outcomex, 365mesh, Lucendus, and Farmdeck, joins them as the company looks to build an Australian cyber security product for domestic and international customers.
The launch comes as companies face a cyber threat environment shaped by artificial intelligence tools that can speed up reconnaissance, automate parts of an attack, and widen the range of exploitable weaknesses. ThreatCanary is positioning its product around that shift, arguing that security teams need a clearer view of how separate weaknesses can be linked.
Rather than focusing on individual alerts, the platform is designed to map internet-facing assets, APIs, identities, cloud links, trust boundaries, and exposed services so organisations can assess how an intruder might move through their systems. This is intended to address a fragmented market in which different tools often examine parts of the problem in isolation.
Platform focus
The offering centres on three core elements. External Attack Surface Management discovers and maps external assets, API Security identifies how interfaces expose data and trust relationships, and Autonomous Offensive Security tests whether those exposures can be turned into a viable attack path.
The platform also includes modules for vulnerability and threat intelligence, dark web monitoring, and asset management. Together, these functions are meant to give customers an ongoing picture of what is exposed, what may already be circulating outside the organisation, and which systems are critical or unmanaged.
One part of the system monitors security advisories, exploit repositories, and technical disclosures across multiple regions and languages, including Chinese and Russian-language research that can be difficult for English-speaking teams to track consistently.
That emphasis reflects a broader cyber security challenge: technical findings often outpace an organisation's ability to decide what matters most. Businesses may have large volumes of vulnerability data but limited evidence about which issues can actually be combined to compromise systems or data.
“Security teams do not need another thousand findings,” said Matt Flannery, Co-Founder and Chief Executive Officer, ThreatCanary. “They need to know which weaknesses can actually be chained into compromise, what attackers would do next, and what to fix first. ThreatCanary is built to give organisations the attacker view continuously.”
API risks
APIs are a particular focus for the founders, who argue that custom-built interfaces can create blind spots because they often sit outside the regular software update cycle associated with packaged applications.
“APIs provide access to databases with sensitive personal information, and these APIs are often custom developed, so they never receive security updates,” said Andrew Horton, Co-Founder and Chief Technology Officer, ThreatCanary. “ThreatCanary has a focus on API Security because APIs are often the weakest link that leads directly to data breaches - the sort that have affected all Australians.”
The company argues that combining asset discovery, API analysis, and offensive testing provides a more practical picture of risk than standalone scans or point-in-time penetration tests. This reflects a broader trend in the security industry towards continuous exposure management rather than periodic assessment.
Delgado said the timing reflects both the pace of AI development and an opportunity for Australian firms to create more of their own cyber security technology. His appointment also adds a founder with experience building and scaling technology businesses across infrastructure, software, and services.
“ThreatCanary is entering the market at the right time,” said Marco Delgado, Co-Founder and Chairman, ThreatCanary. “AI is changing both the speed of attack and the expectations placed on teams. We believe Australia has the talent to build globally relevant cyber security companies, and ThreatCanary has the technical depth, product ambition, and execution focus to compete on that stage. Australia should not simply consume the next generation of AI. We should build it, own it, and control it.
“Our vision is to advance sovereign AI cyber security capability built here in Australia, grounded in Australian-based knowledge, threat intelligence, business environments, and operational realities. By combining advanced AI with secure agentic systems purpose-built for Australia, we can ensure these technologies understand the unique requirements, risks, regulatory landscape, and operating context of Australian businesses.”
Horton said the company aims to provide a persistent layer of offensive security that helps organisations understand exposure as it changes.
“Through Australian ingenuity, ThreatCanary now delivers the continuous offensive security layer needed for modern organisations: one platform that discovers what is exposed, understands how systems connect, creates the tests needed to prove risk, and continuously validates how attackers could move,” he said.