

Secure.com says ransomware budgets should fix basics first
Sat, 17th Oct 2026 (Today)
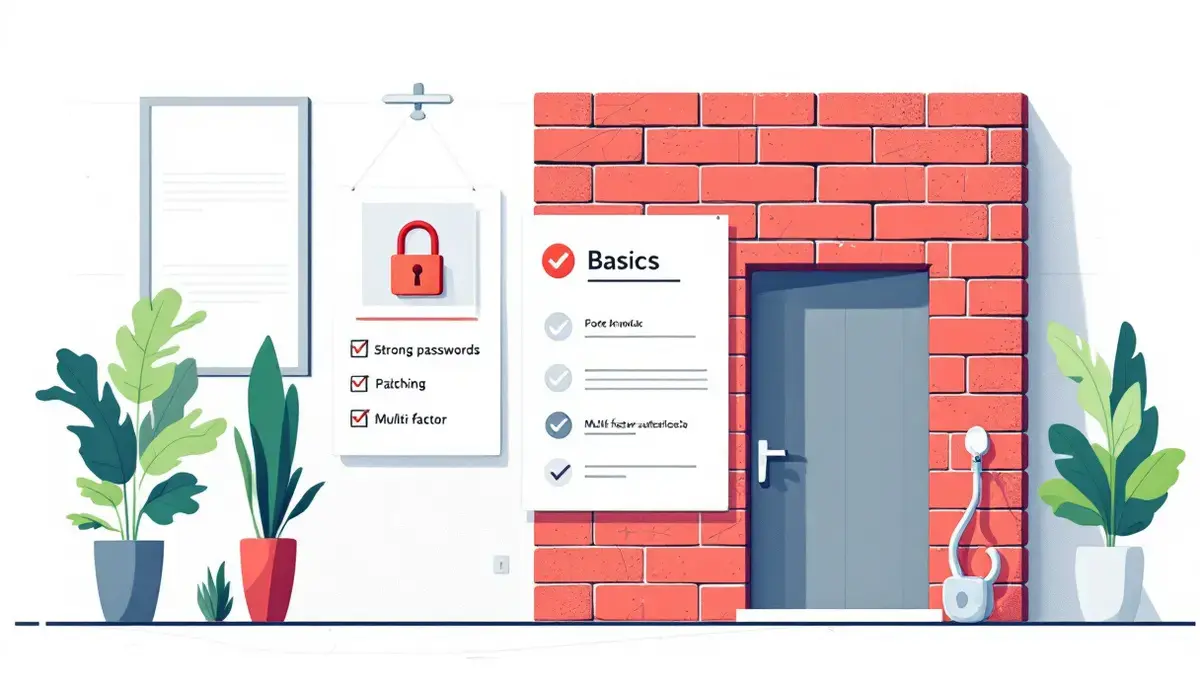
Secure.com has published an analysis arguing that ransomware budgets should focus on basic security gaps rather than artificial intelligence threats. It says the main entry points for ransomware remain stolen passwords, unpatched internet-facing systems and phishing.
Written by Waseem Ahmed, Head of Engineering at Secure.com, the piece presents AI as a tool that can speed up some parts of an attack without changing the main causes of breaches. It argues that security teams and managed service providers should prioritise spending on identity controls, patching, attack-surface visibility, detection and backups before directing money towards what it calls AI-related hype.
Ransomware became a major criminal business long before modern generative AI tools were released to the public. The paper cites the 2017 WannaCry outbreak, which affected more than 300,000 computers across 150 countries, as evidence that cyber criminals had already built scalable ransomware operations before current AI tools became widely available.
It also cites research identifying 277 ransomware gangs between 2015 and 2025, with 102 active in 2025 alone. Over the same period, ransomware remained one of the most common forms of cyber crime affecting organisations. Verizon's 2025 Data Breach Investigations Report found ransomware in 44% of all breaches, up from 32% a year earlier.
Known weaknesses
A central theme of the analysis is that attackers still rely on routine weaknesses rather than novel methods. It identifies three recurring access routes: stolen or weak credentials, software vulnerabilities in internet-exposed systems, and phishing or other forms of social engineering.
According to the figures cited, stolen credentials were linked to 22% of breaches in Verizon's 2025 report. Exploitation of known vulnerabilities accounted for 20%, while 16% began with a person being deceived.
The paper gives particular attention to perimeter devices such as VPNs and firewalls. Based on Verizon's findings, attacks on VPNs and edge devices increased nearly eightfold in a year, while Coalition traced 58% of its ransomware claims to problems involving the same types of devices.
Ahmed uses a recent retail cyber incident to illustrate how simple the initial compromise can be. The analysis refers to an attack on Marks & Spencer in which a password reset was allegedly obtained by someone posing as a member of staff in a help desk interaction, leading to an estimated profit hit of about £300 million.
AI's role
The report does not dismiss AI as irrelevant to cyber crime. Instead, it says AI can help attackers produce more convincing phishing emails, improve poor-quality malware code and map target networks more quickly after gaining access.
Its argument is that these uses do not remove the need for an initial entry point. In this view, AI may improve efficiency for criminals, but it does not replace the need for a stolen password, a successful phishing attempt or an unpatched exposed system.
"The smart budget move is plain. Pay to close the doors you already have, not to fight a robot attacker that isn't hurting you," said Waseem Ahmed, Head of Engineering at Secure.com.
Ahmed also draws on language used by threat researchers to describe the current state of AI in ransomware operations. "People tracking these groups describe AI today as an accelerant, not a revolution," he said.
Budget priorities
The analysis sets out a spending order it says offers the highest return for organisations trying to reduce ransomware risk. At the top of the list is identity security, including multi-factor authentication and the removal of shared logins, to make stolen passwords less useful.
Next comes patching internet-facing systems, especially VPNs, firewalls and public servers. The paper then calls for better visibility of attack surfaces so companies know which systems are exposed and can address them before attackers find them.
It also recommends investing in rapid detection and response, on the assumption that some intrusions will still occur, as well as tested backups that attackers cannot easily reach. Supplier risk is another area it highlights, reflecting the growing use of external partners and vendors as an access route into larger organisations.
For smaller security teams, the paper argues that the first steps should be stronger authentication and better protection for internet-exposed systems. It says this approach closes many of the most common access routes without requiring large spending on new tools.
The analysis also questions whether companies should budget to pay extortion demands. It says recovery costs often outweigh ransom payments and cites Sophos research estimating the average recovery bill, excluding ransom, at USD $1.53 million in 2025.
Ahmed's broader point is that boards and security leaders should base cyber budgets on the causes of actual losses rather than headline-driven fears. Secure.com argues that the most effective defences are still the least novel: stronger identity checks, faster patching, clearer visibility and reliable recovery plans.
The paper concludes that while AI can assist defenders as well as attackers, the biggest gains in ransomware prevention still come from addressing routine weaknesses that have remained largely unchanged for years.