
PHP flaws spark emergency patch warning for websites
Fri, 23rd Oct 2026 (Today)
Cyber security specialists have urged organisations running PHP-based websites to install emergency updates or take exposed systems offline. The warnings follow the disclosure of critical flaws in the widely used web scripting language.
The vulnerabilities affect PHP itself rather than a single application built on top of it, giving the issue broad reach across websites, content management systems and other internet-facing services that rely on PHP to process web requests.
Tenable gave the flaws its highest internal severity rating, saying they could allow unauthenticated remote code execution if exploited. One of the vulnerabilities could also expose memory.
Security researchers compared the scale of the problem with Log4Shell, the software flaw that triggered a global scramble across corporate and government networks. They said the response this time may differ because PHP is easier for most organisations to identify in their own estates than hidden Java logging libraries were during the Log4j crisis.
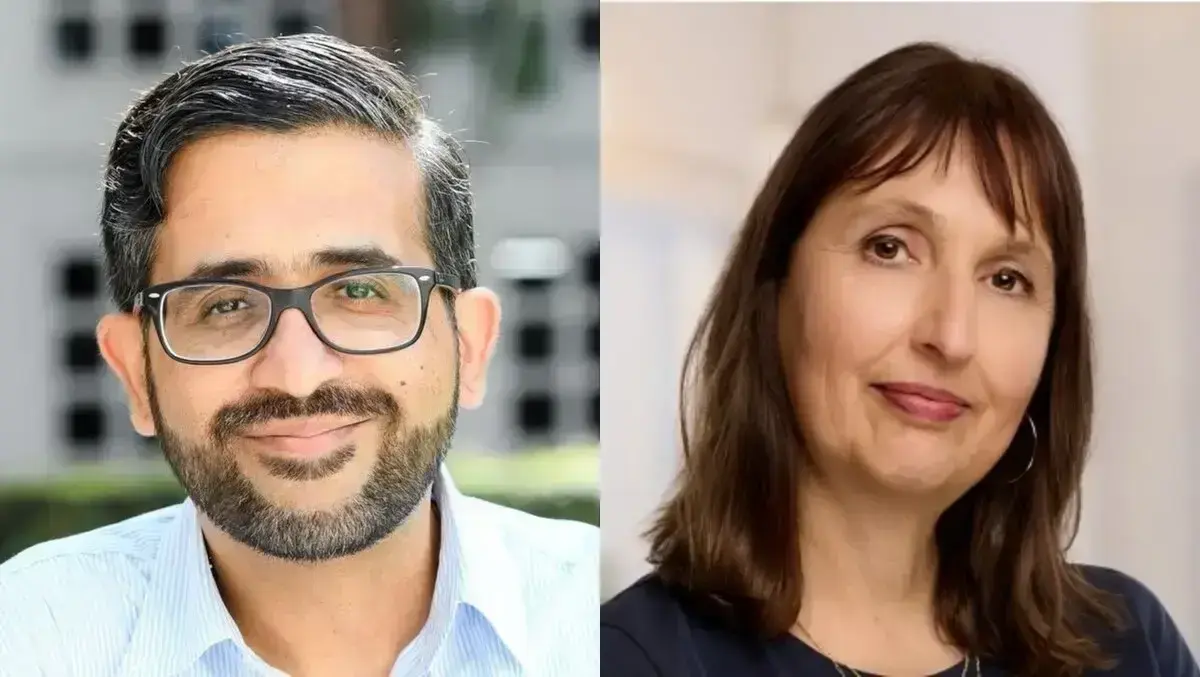
"PHP2Shell has many of the same ingredients as Log4Shell: unauthenticated remote code execution in software that runs almost everywhere, triggered by a single crafted request. But it plays out differently. Log4j was buried deep in Java dependencies, and teams spent weeks just finding it. PHP is easier to spot, so organizations can find exposures faster. And contrary to Log4Shell, there is already a patch available. The PHP bugs are also harder to exploit than Log4Shell, but now that a working exploit exists, that won't slow attackers down for long. Security teams should immediately patch internet-facing PHP systems and then verify that those fixes actually hold," said Deborah Galea, Senior Product Marketing Manager, Filigran.
Patch race
A public exploit has sharpened concern among defenders. Security teams are now under pressure not only to deploy updates but also to identify every external system that might still expose a vulnerable PHP installation.
"Publishing a working PHP2Shell exploit before the official fix was available was not research. It handed attackers a head start while defenders had nothing to deploy. Coordinated disclosure exists to avoid this. Now that the exploit is public, the first priority is knowing your attack surface: which PHP endpoints are actually reachable from the internet, including forgotten legacy systems, and whether existing protections sit in the path. The second is ownership and impact. Every exposed asset needs an owner who can act immediately, and an understanding of what a compromise would mean, whether customer data, credentials or a foothold into the internal network. Severity scores alone rank every PHP server the same. Emergencies like this one don't test how fast organizations read advisories; they test whether they already knew their exposure before the advisory dropped," said Mathieu Rigotoo, Chief Information Security Officer, Filigran.
PHP's prevalence makes remediation difficult, Tenable said. Estimates it cited suggest that nearly 70% of websites with a known server-side language run PHP. That figure does not show which versions are in use, and that uncertainty complicates efforts to measure exposure quickly.
Satnam Narang, Senior Staff Research Engineer at Tenable, said the vulnerabilities were among the most consequential since Log4Shell because of their reach and scope. He added that exploitation attempts were already being reported and working exploits were likely to spread quickly among attackers.
Long tail
The speed of patching is likely to vary sharply across the market. Mainstream Linux distributions and long-term support vendors were given advance notice, according to Tenable, so updated packages could arrive within hours or days. Systems running unsupported versions of PHP face a much longer wait, and some may never receive a fix.
Bundled software packages may prove harder to secure. Organisations using products that contain PHP often need to wait for the software vendor to issue its own update. Cloud-hosted services may be patched faster, while self-hosted and on-premises systems depend on in-house administrators to identify, schedule and complete the work.
Tenable also noted that the vulnerabilities were discovered with AI assistance. Narang said that trend is increasing the volume of flaws surfacing across the security industry, even if only a small number match the severity of the PHP issue facing website operators worldwide.