

Keeper & SailPoint link up to automate access control
Fri, 2nd Oct 2026 (Today)
Keeper Security has integrated its privileged access management platform with SailPoint's identity governance and administration system to automate how access rights are granted and removed across Keeper-managed accounts and resources.
The integration uses the Keeper SaaS Connector to link SailPoint's IGA platform directly with KeeperPAM. Through that connection, SailPoint can manage the provisioning, deprovisioning and entitlements of Keeper users, vaults and managed resources.
For many organisations, identity governance and privileged access management have operated as separate systems, with one defining who should have access and the other enforcing it. That split has often left security teams to handle role changes, revocations and offboarding manually inside password vaults and privileged access tools.
Manual processes can leave credentials behind when staff change roles or leave a business. Without a direct link between governance and privileged access systems, reviews and clean-up work can also be slower and less consistent.
Closing gaps
Keeper cited its 2026 research, which found that 96% of senior IT leaders said disconnected security tools were creating exploitable gaps. It also found that 64% of respondents were not yet operating with fully consolidated privileged access governance.
Under the integration, roles and entitlements defined in SailPoint are provisioned automatically into Keeper across team memberships, shared folders, roles, nodes, records and administrative permissions. Organisations can choose which entitlement types SailPoint manages within the system.
The arrangement is intended to preserve Keeper's zero-knowledge design, meaning credentials are not exposed to SailPoint during the process. Every grant, update and revocation is also logged automatically across both platforms.
Audit trail
The companies are also aiming to address a longstanding audit issue in privileged access management. When SailPoint runs scheduled access certifications, the review can now include the privileged credentials, non-human identities and identities managed by Keeper, giving auditors a reconciled record across the two systems.
That may be particularly relevant for heavily regulated sectors and public bodies that need evidence of account management, least-privilege controls and tighter handling of privileged credentials. According to Keeper, the integration supports compliance requirements tied to NIST Special Publication 800-53 Rev. 5 for federal agencies.
Keeper added that it holds FedRAMP High certification, FIPS 140-3 validation and a place on the CISA Continuous Diagnostics and Mitigation Approved Products List. Those accreditations are likely to matter in procurement processes where public sector buyers assess how access control systems align with government security standards.
Market context
The tie-up reflects a broader shift in cybersecurity spending towards identity-based controls as companies try to limit the damage from compromised accounts, machine credentials and administrator privileges. Privileged access management tools have become more central to that effort as businesses seek tighter control over who can access sensitive systems and when.
Identity governance products, meanwhile, are increasingly expected to do more than oversee approval workflows and periodic access reviews. Buyers want direct enforcement links so governance decisions lead to immediate operational changes rather than tickets and manual follow-up work for security teams.
The integration is available now for organisations using SailPoint for identity governance and KeeperPAM for privileged access management. Keeper described the link as a way to remove the reconciliation work that has typically sat between the two systems.
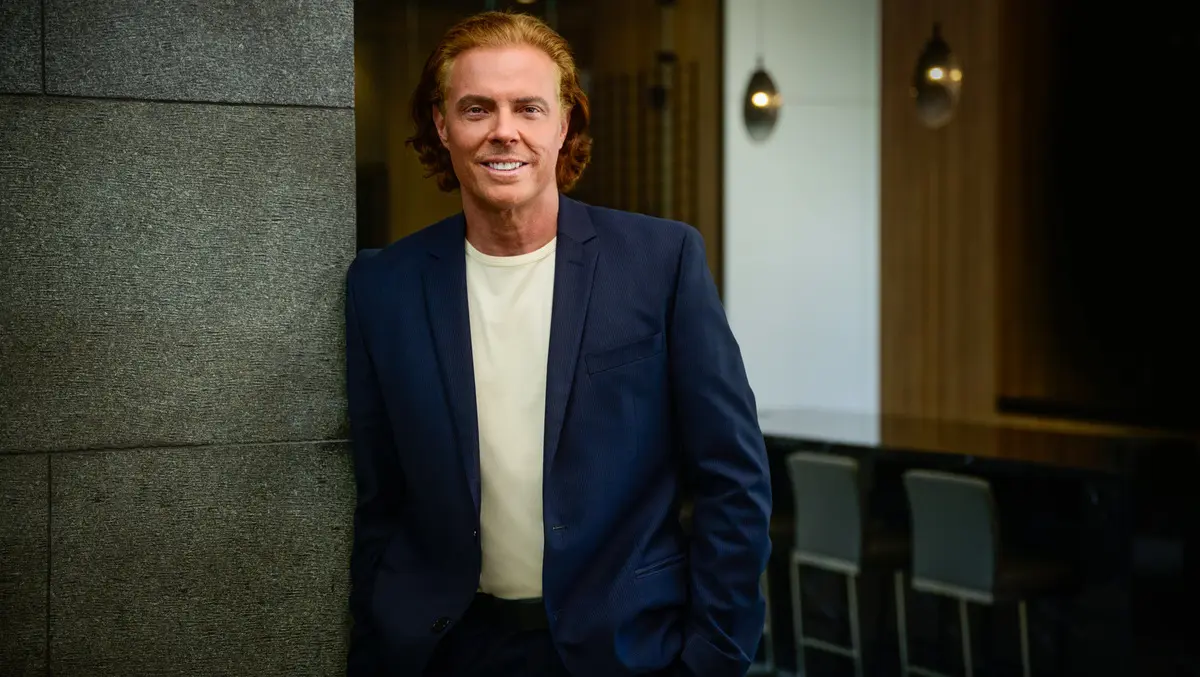
"The organisations that properly implement identity security understand that governance is only as strong as its enforcement," said Darren Guccione, Chief Executive Officer and Co-Founder of Keeper Security.
"Seamless integration between IGA and PAM covering any type of human and non-human identity is an enormous gap for most enterprises. Our integration with SailPoint solves this," Guccione said.