

Keeper launches Freshservice workflow for access approvals
Tue, 6th Oct 2026 (Today)
Keeper Security has launched a Freshservice Workflow integration that links vault and privileged access requests with the Freshservice ticketing system.
The integration lets IT and security teams search Keeper vault content and manage access requests from a Freshservice ticket sidebar. It also supports approval requests tied to Keeper's Endpoint Privilege Manager and Cloud SSO device approvals.
Access approvals often require service desk staff to leave a ticket, sign in to another system, and find the relevant record before granting permission. That can slow response times and push decision-making into email or chat, where maintaining a full audit trail may be harder.
Under the new setup, an employee submits a request through a Freshservice service catalogue item. The assigned agent can then search Keeper content, set permissions, and approve or deny the request within the ticket. Each action runs through a customer-hosted Keeper Commander ServiceMode endpoint, rather than storing credentials in Freshservice.
Audit trail
The integration is aimed at organisations that want to keep access decisions within established service management workflows while maintaining oversight of privileged access requests. By placing approval actions in the helpdesk environment, Keeper aims to reduce manual handoffs between service desk and security tools.
The design preserves Keeper's zero-knowledge encryption approach by keeping the cryptographic boundary within customer-controlled Keeper infrastructure. In practice, Freshservice serves as the interface for requests, while the underlying secrets remain outside the ticketing system.
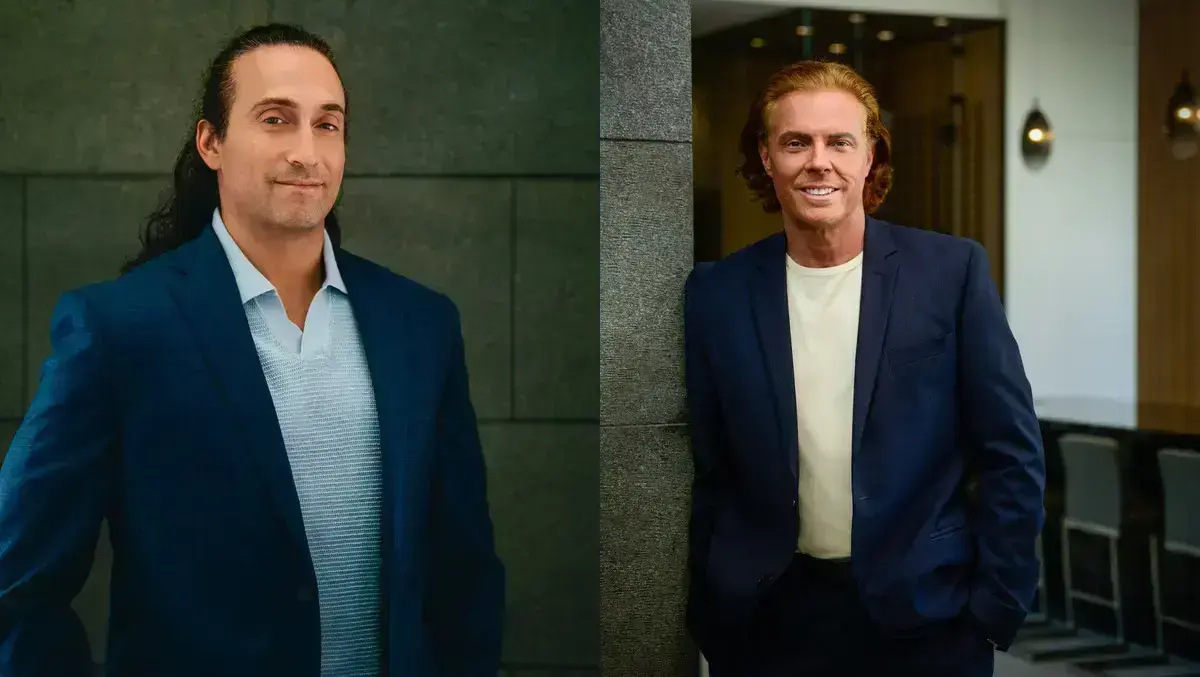
Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security, said that separation is central to the integration.
"The cryptographic boundary cannot move outside Keeper," said Craig Lurey, Chief Technology Officer and Co-founder of Keeper Security.
"This integration processes every approval through Commander ServiceMode on infrastructure owned and controlled by the customer, so the attack surface doesn't expand when you wire Freshservice into your approval workflow. Freshservice is the interface for the request, never the place where secrets are stored," Lurey said.
Single interface
The integration also works alongside Keeper's ITSM for Freshservice app, giving security administrators a single interface for incident-driven access requests and routine approval tasks. That includes device approvals linked to endpoint privilege and single sign-on controls.
The announcement reflects a broader push across the security market to tie privileged access management more closely to day-to-day IT service operations. Vendors have increasingly focused on reducing friction between identity controls and support workflows as companies try to tighten oversight without slowing internal service teams.
Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security, said the issue is not just operational but also tied to governance.
"Every access request is an identity decision, and the further those decisions drift from a governed system, the weaker the audit trail becomes," said Darren Guccione, Chief Executive Officer and Co-founder of Keeper Security.
"Integrating Keeper into Freshservice keeps approval decisions inside a ticketing system that security teams already trust, which means zero standing privilege and full audit control stay intact. This becomes increasingly important in the agentic era, as access requests multiply across both human and machine identities," Guccione said.
The Freshservice Workflow app is available through the Freshworks Marketplace for organisations with an active Keeper Commander deployment. Its release gives companies already using Freshservice another way to connect service desk tasks with privileged access controls without moving agents out of the ticket they are working on.