

Hexnode has expanded its XDR product with new threat detection, alert prioritisation and remediation features, and added macOS support alongside Windows.
The changes are aimed at IT and security teams that need to investigate threats and respond with fewer manual steps. Hexnode, the software division of Mitsogo, has more closely linked the product with its unified endpoint management platform so security investigations can connect directly to actions on affected devices.
New additions include integrations with Mandiant and Recorded Future, allowing endpoint activity to be checked against external threat intelligence sources. The updated service also includes sandbox analysis for suspicious files and anomaly detection designed to flag unusual behaviour that may not match known threat signatures.
Hexnode has also added severity-based alert ranking and dynamic risk scoring for devices to help analysts decide which incidents and endpoints need attention first. Administrators can set exclusion policies for trusted files, applications and processes to reduce false positives.
New response tools include endpoint isolation, vulnerability management and automated remediation. Endpoint isolation cuts a device off from the network while keeping it manageable through Hexnode. Vulnerability management links incident investigation with patching through the company's endpoint management system.
Automated remediation uses predefined rules and policies to trigger corrective actions without requiring each step to be carried out manually. Custom dashboards have also been added so teams can tailor monitoring views to different roles and priorities.
Hexnode XDR also integrates with Splunk and QRadar, allowing organisations to connect the product with existing security information and event management systems for broader investigation and reporting. The latest changes extend the product's reach beyond Windows devices with support for Apple's desktop operating system.
Security operations spending remains a focus for many organisations in Australia and New Zealand. According to figures cited by Hexnode, 68% of organisations across the two markets expect to increase spending on security operations centre functions.
The update follows the earlier launch of Hexnode XDR and reflects a broader push by security software suppliers to tie detection more closely to operational response. In practice, that means giving analysts more context around an alert and a direct path to contain a device, identify missing patches and apply a fix.
Pressure on Teams
Security teams often face a high volume of alerts, many of which require triage before action can begin. XDR products have increasingly focused on reducing that workload by ranking incidents, bringing together signals from multiple tools and automating repeatable response tasks.
Hexnode's additions include AI-assisted investigation through its Genie AI tool, which provides plain-language alert summaries and uses incident data to explain what happened, identify what is affected and recommend a fix. It described alert prioritisation, asset scoring and automated remediation as building blocks for broader AI-assisted security operations workflows.
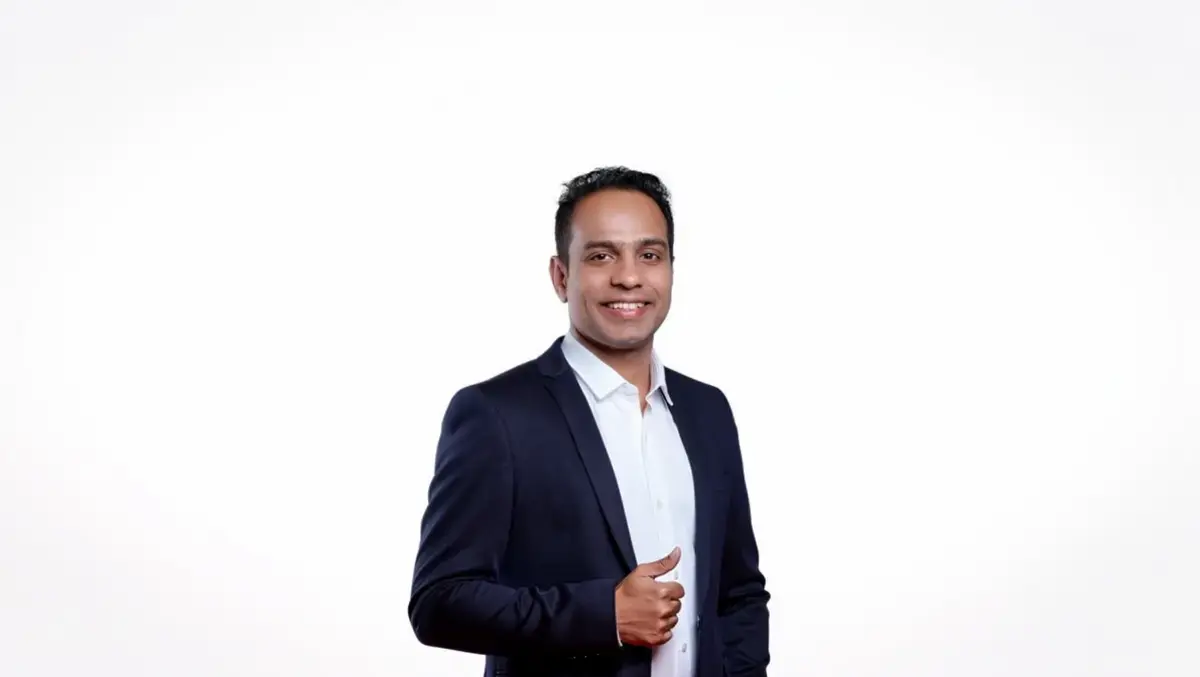
Apu Pavithran outlined the company's view of the problem in a keynote address.
"We built Hexnode XDR around one complaint we heard constantly: security tools are good at telling you something is wrong, and bad at helping you do anything about it. More alerts was never the request. Fewer steps between the alert and the fix - that was the request," said Apu Pavithran, Chief Executive Officer and Founder, Hexnode.
Hexnode's approach is to combine threat detection, device intelligence and endpoint management in one workflow so teams can move from investigation to containment and remediation without switching between separate systems. That includes one-click device isolation, patching tied to vulnerabilities found during incidents and policy-based corrective actions triggered automatically.
The expansion also reflects growing demand for cross-platform endpoint security as organisations manage mixed estates of Windows and macOS devices. By extending support to macOS, Hexnode is widening the number of endpoints that can be monitored and acted on through the same XDR system.
Integrations with third-party intelligence feeds and SIEM tools also suggest Hexnode is aiming to fit into existing security stacks rather than require organisations to replace established monitoring tools. The combination of incident context, prioritised alerts and linked response actions is intended to narrow the gap between identifying suspicious activity and acting on the affected endpoint.