

Fortinet: The AI challenge is visibility and control, not permission
Fri, 16th Oct 2026 (Today)
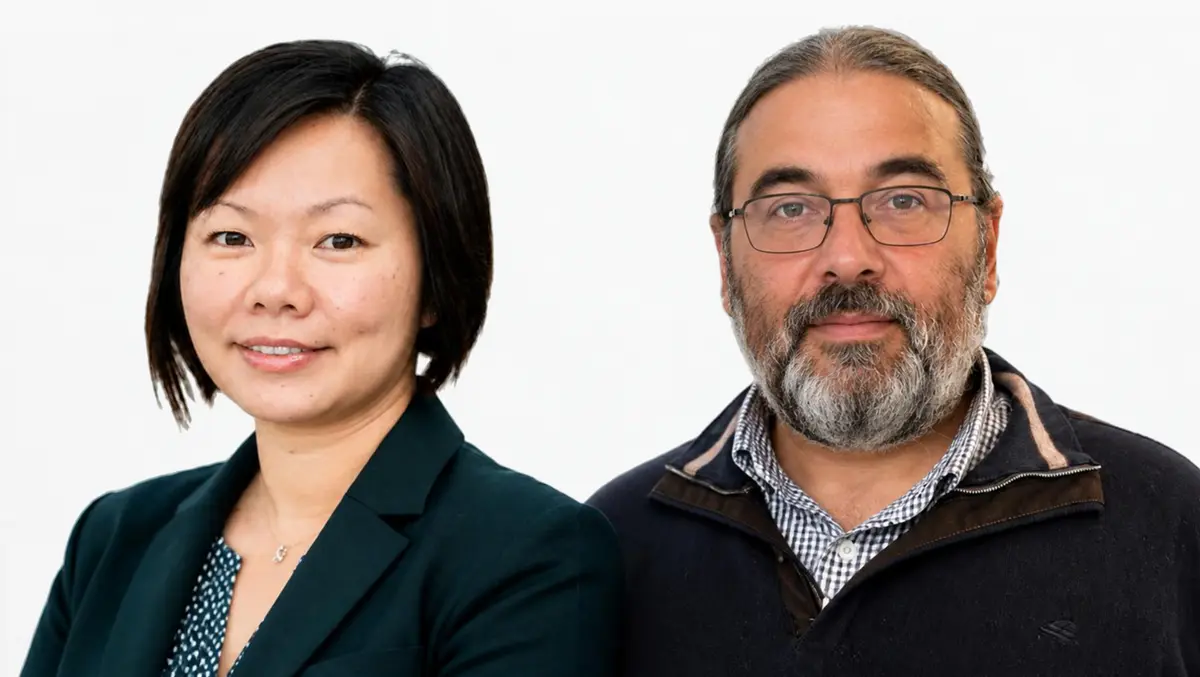
The world at large has moved past the question of whether to allow artificial intelligence in the workplace, tackling instead the issue of whether IT and security teams can see, understand, and control how AI interacts with data, applications, and infrastructure. That's according to Fortinet senior executives Wei Ling Neo (VP, Product Management and R&D) and Filippo Cassini (Global Technology Officer, Senior VP of Engineering).
The shift mirrors previous shadow IT challenges, but with enhanced pace and risk. In a classic case of the genie being well out of the bottle, it's fair to say everyone is using AI. Fair too, that not everyone is upfront and open about that use, and what can't be measured can't be managed. And what isn't seen, can't be secured.
"Essentially, users are leveraging whatever tools they find useful, and today that means agents," said Neo. "While this helps productivity, it also leads to sprawl; combine that with frontier models which commoditise vulnerabilities and cyberattacks, with every agent potentially presenting a weakness, and you have a problem."
Commoditisation of AI
Cassini said the emergence and rapid maturation of AI tools builds on the commoditisation of IT trend noted several years ago. "The way AI has come into the enterprise is partially why it has proliferated so rapidly, but is also part of why it is now becoming an issue to be managed," he observed. "With many tools available free, or well under expense thresholds, staff use personal accounts or simply expense them."
It isn't, he agreed, difficult to see how data-exposure and compliance risks quickly eventuate.
Industry research underscores the scale of the problem, with Gartner identifying shadow AI as a top risk for enterprise leaders. The market watcher has cautioned that by 2030 some 40 percent of organisations could experience security or compliance incidents linked to shadow IT, while also noting that 69 percent of cybersecurity leaders already suspect or have evidence of employees using prohibited generative AI services. (It's not all bad: Gartner also noted shadow IT isn't a problem per se, it's the absence of control that is.)
Moreover, agent sprawl as flagged by Neo, is expected to intensify. While this is intuitive, Gartner's projections quantify the issue, with an anticipation that a typical Fortune 500 enterprise could have more than 150,000 agents in use by 2028. Experience points to the possibility that these estimates may yet prove conservative.
Organisations invest in cybersecurity because breaches aren't free. IBM's Cost of a Data Breach study ran the ruler against organisations with high levels of shadow AI, finding that on average this factor results in costs around $670,000 higher than those with low or no shadow AI exposure.
Ban, or enable
While the ban hammer is in the toolbox, it is a blunt instrument with demonstrably limited effect, and in any case the horse has already bolted. "Blocking these applications is not necessarily useful," said Neo. "Instead, visibility is where it starts. Our customers recognise this, and are moving in favour of visibility and selective enforcement. With insight into usage, they can identify preferred providers, establish clear parameters, and apply tighter controls."
The practical path for customers combines visibility, policy, and coaching rather than prohibition. A clear AI compliance policy provides the baseline, but Neo stressed that "having a policy doesn't mean that staff read the policy." Endpoint coaching, data-loss-prevention rules applied to generative AI interactions, and risk scoring of applications help translate guidelines into daily behaviour, helping organisations to retain the productivity benefits of AI while reducing the risks.
On the subject of control, Cassini described a progression: understand the scale of AI use, form partnerships with sanctioned tools, and only then lock down the rest.
The measures Fortinet provides include virtual patching which accelerates response times by applying immediate protections when vulnerabilities emerge, ahead of formal upgrades. On the detection and response side, an agentic stack allows security operations teams to run playbooks, parse logs, and triage faster.
Heterogeneous environments complicate the picture. Cassini and Neo explained that FortiGate serves as a network conduit, gaining visibility of shadow AI activity. In mixed-vendor settings, MCP servers are exposed allowing agentic management of underlying components in accordance with approved policy. For organisations building their own AI infrastructure, additional layers matter: secure enclosures, web application firewalls such as FortiWeb, API protections, and specialised controls (including FortiAIGate) that inspect prompts and responses to limit leakage or prompt-injection risks while models run.
If not AI, then quantum
Cassini said there is growing appreciation of the emerging and existing threats posed by AI. "A lot of our enterprises do see the risk. The problem really comes down to getting better visibility, then adjusting and accommodating for what the business needs…and understanding where important data is being used by AI agents and applications."
Finally, while AI is the dominant topic in information security (and nearly everywhere else), it too will become part of the background noise like digital transformation, big data, and consumerisation of IT.
What's next may well be quantum computing. But whatever it is, with a smile Neo said. "It's never a dull moment for infosec. Attackers and defenders have the same productivity multiplier, and success depends on being able to observe, identify and control everything that matters in their digital environments."