

Australia & New Zealand urged to act on cyber risks
Thu, 1st Oct 2026
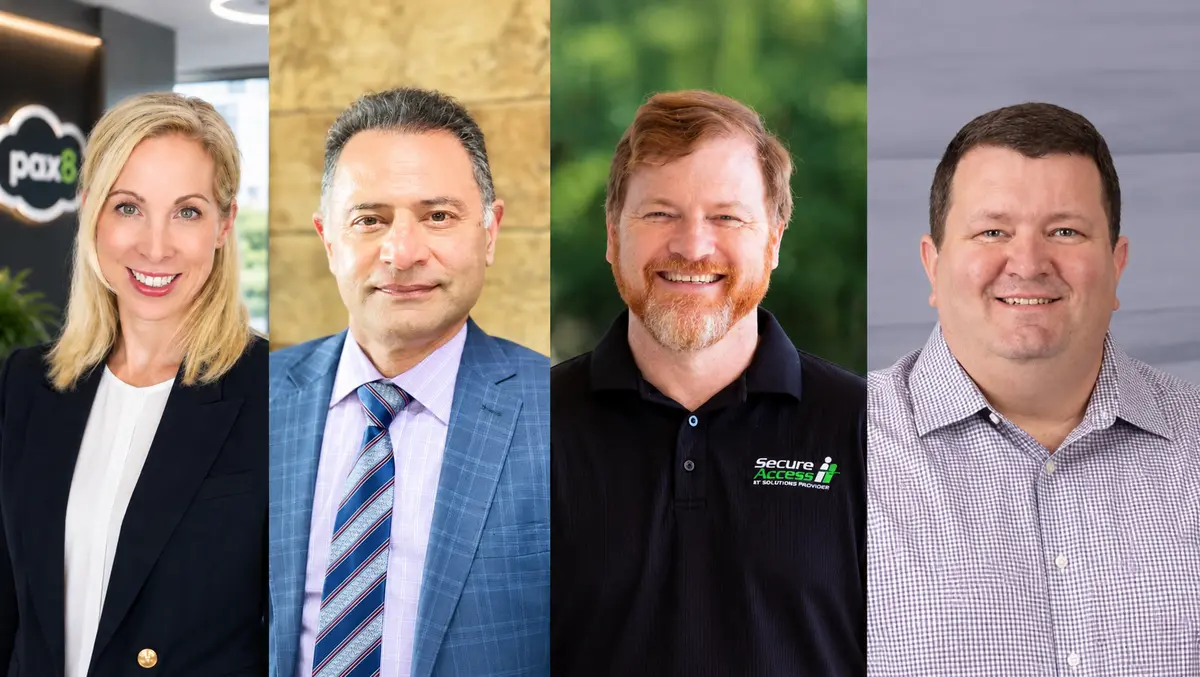
Security vendors and industry groups across Australia and New Zealand are urging businesses to use this year's Cyber Security Awareness Month as a prompt for concrete action. Executives from Sectigo, Nutanix, GTIA, Pax8 and Tanium warn that smaller organisations and mid-market firms remain exposed as attack surfaces expand and AI adoption accelerates.
Quantum-era risks are emerging as a central concern. Jason Soroko, Senior Fellow at Sectigo, said organisations cannot treat preparation for post-quantum cryptography as a one-off project they can switch on later.
"Quantum readiness isn't a switch you flip overnight. It's a continuous, uneven migration across every system an organization owns. The first step is understanding where cryptography exists across the environment, but inventory alone isn't enough. Organisations also need context to understand which cryptographic assets support critical systems, where the greatest risks lie, and what should be prioritized first. With that visibility and understanding, they can take a risk-based approach to planning and build the crypto agility needed to adapt as cryptographic standards evolve. Quantum readiness isn't about fixing everything at once. It's about making informed decisions and steadily reducing risk over time," said Jason Soroko, Senior Fellow at Sectigo.
Infrastructure complexity is also driving concern about basic visibility. Daryush Ashjari, Chief Technology Officer and Vice President of Solution Engineering APJ at Nutanix, said organisations are struggling with blind spots across hybrid multicloud and distributed environments as they add AI and edge workloads.
"As we recognise Cybersecurity Awareness Month, organisations should acknowledge that cybersecurity blind spots are no longer limited to external threats. As businesses accelerate their adoption of hybrid multicloud architectures, AI platforms, edge computing, and distributed applications, maintaining visibility across what needs to be secured is becoming increasingly challenging.
"The challenge today is not simply keeping bad actors out. It is understanding where critical data resides, how it moves across cloud and on-premises environments, and who or what has access to it. Every new cloud service, AI deployment, or edge workload expands the attack surface and creates new opportunities for security gaps to emerge. Without a comprehensive view of the environment, risk becomes harder to identify, manage, and mitigate. Visibility is the foundation of cyber resilience in the hybrid multicloud era. Organisations cannot effectively protect, govern, or recover assets they cannot see. Security leaders need a unified view across infrastructure, applications, identities, and data, regardless of where they reside.
"This visibility enables faster threat detection, stronger governance, and more effective response when incidents occur. To strengthen resilience, organisations should focus on a few key priorities.
"First, simplify security operations by establishing consistent policies and controls across environments. Second, adopt a data-centric approach to security by understanding where sensitive information lives and ensuring it is protected throughout its lifecycle. Third, implement Zero Trust principles that continuously verify users, devices, and workloads rather than assuming trust based on network location. Finally, ensure cyber recovery capabilities are regularly tested so critical services and data can be restored quickly in the event of disruption.
"The organisations best positioned to navigate the evolving threat landscape will be those that can reduce complexity, maintain end-to-end visibility, and build resilience into every layer of their hybrid multicloud strategy. In an environment where threats continue to evolve and technology estates continue to expand, visibility is no longer just a security requirement. It is a business imperative," said Daryush Ashjari, Chief Technology Officer and Vice President of Solution Engineering APJ at Nutanix.
Small and mid-sized businesses remain in the spotlight on both sides of the Tasman. Jason Garland, Director at Secure Access IT and GTIA ANZ Executive Council Member, pointed to rising incident costs and attack rates for small firms in Australia and New Zealand, and said responsibility is falling heavily on managed service providers.
"Cybersecurity Awareness Month is a good time to look at who carries the most risk. In Australia, small businesses reported an average loss of $56,000 per cybercrime in 2024-25, up 14 per cent on the previous year. In New Zealand, 53 per cent of SMEs faced a cyber threat or attack in the past six months, rising to 76 per cent among businesses with 20 to 49 staff. This year's theme, 'take a second, stay secure', sounds simple, but small businesses don't have the time, budget, or expertise to stay secure on their own. They rely on their IT service provider (ITSP) to spot the risks they miss, which puts ITSPs squarely on the front line.
"Many ITSPs serving small and mid-sized businesses are small businesses themselves. They face the same skills shortages and cost pressures as their customers while managing security for dozens of clients at once. Vendors, distributors, and industry bodies need to make it easier for these providers to access training, share threat intelligence, and build services that fit SMB budgets.
"Better support for ITSPs and better protection for SMBs depend on the entire IT ecosystem working together. When knowledge is shared and peers are connected, threats are identified sooner, gaps are closed faster, and good practice spreads further. No business, big or small, should face these risks alone, so I encourage every organisation to use this month to review its own security, talk to clients, customers, partners, and peers, and make sure no business is left without support," said Jason Garland, Director at Secure Access IT and GTIA ANZ Executive Council Member.
Vendors focused on the mid-market say economic pressure and uncertainty about AI are slowing some security improvements. Lindsay Keating, Executive Vice President and General Manager APAC at Pax8, said many owners still see AI as risky despite its potential benefits.
"Midsize companies and SMBs are often seen as easier targets for cyber criminals. While enterprises are investing funds and resources in preventative measures, organisation-wide training, and the latest technologies, midsize companies and SMB owners are focused on simply keeping the business running amid economic uncertainty and a cost-of-living crisis.
"AI presents an unprecedented opportunity for companies to compete, grow, and secure their organisations at the same pace and scale as enterprises, but many business owners across ANZ are hesitating to act, too concerned about potential backlash or a general fear of change. This Cyber Security Awareness Month, which the Australian government is encouraging companies to treat as a year of action, couldn't be more timely. Taking action doesn't need to mean adopting every AI tool for the sake of it. In fact, for midsize and SMB owners, a savvier place to start is education. Knowledge is power, and the more we can equip businesses with the information needed to make smart, effective, and strategic AI investments, the more resilient they will be against cyber threats," said Lindsay Keating, Executive Vice President and General Manager APAC at Pax8.
AI is also reshaping how larger organisations manage cyber risk. James Greenwood, Area Vice President of Solution Engineering APAC at Tanium, said many enterprises have yet to match AI-driven insight with operational follow-through.
"This year, the ASD is calling for an inaugural year of action, and for good reason. Many businesses are already using AI to uncover insights around market opportunities, growth prospects, and of course, cyber threats. But few organisations are using AI to turn those insights, dashboards, and data into tangible action. This gap will separate the AI experimenters from the AI adopters, with the latter best equipped to turn noise into action plans specific to their roles.
"We're now in a world where both skilled and less skilled operators can enter a prompt for an IT or security issue and be directed on how to address that issue in real time, lowering the need for highly skilled resources and democratising access to tools. Management has never had greater access to real-time reporting and visibility, as well as comprehensive guidance on how to investigate, mitigate, and remediate issues as they happen.
"Taking effective control of these new capabilities requires companies to pair their AI adoption with a 'human above the loop', not just a 'human in the loop'. We can't afford to assume that equipping our teams with AI will lead to good governance. Businesses need to ensure that, alongside controlled AI adoption, there is a proactive approach to keeping humans in control of how AI is used, designed, and evolved over time. This means not being afraid to change, stop, or update AI tools and approaches as needed, and investing the time and resources to ensure they operate in ways that support and strengthen cyber hygiene without introducing new business or governance risks," said James Greenwood, Area Vice President of Solution Engineering APAC at Tanium.